Block destructive SQL
DELETE and UPDATE without WHERE, DROP, TRUNCATE and risky DDL, inside CTEs and in every statement of a multi-statement string too. Every block comes with the rule, the AST node and a suggested fix.
Connect it as a TCP proxy, an API, the CLI or MCP. Vericto parses each query's AST and blocks destructive operations before they reach your database.
DELETE FROM users
BLOCKEDVERICTO-001DELETE without WHERE: it never reaches the database. The agent gets an SQL error and the suggested fix.
DELETE FROM users WHERE id = $1
SELECT email FROM customers
MASKEDVERICTO-085email is a sensitive column: the proxy rewrites the query and the database returns the masked value.
a***@example.com
SELECT id, total FROM orders WHERE id = $1
ALLOWEDorders is in the agent's allowlist: the query passes untouched.
id · total
A deterministic AST engine decides on every statement before it runs. Four controls run on top of it.
DELETE and UPDATE without WHERE, DROP, TRUNCATE and risky DDL, inside CTEs and in every statement of a multi-statement string too. Every block comes with the rule, the AST node and a suggested fix.
Tag columns such as email or card_number and decide per column: block, flag or mask (full, last4, email or hash). Through the TCP proxy, the database returns the value already masked. Team and Enterprise.
Each agent uses only the tables and columns you give it, read-only or read-write. Everything else is denied. Start in observe and switch to enforce once the traffic confirms it. Team and Enterprise.
Replay a rule change against your real traffic (up to 30, 90 or 180 days depending on the plan) and see which legitimate flows it would block, before it blocks anything. From the dashboard or from CI. Builder, Team and Enterprise.
The panels reproduce the output as the docs describe it; the data is sample data.
Each scenario is a concrete SQL pattern a rule catches, tested against vericto-engine 4.1.1. It is counted once, not once per dialect or per position.
The same rule stops a person's mistake, an ORM bug and a compromised agent's attack. Each scenario is counted under its most typical origin:
A DELETE hidden in a CTE, a tautology in a derived table or a UNION arm, a DROP stacked after a COMMIT, an INSERT … SELECT inside a SQLite trigger: the engine walks the syntax tree down to 50 levels and evaluates every statement of a multi-statement string. Anything deeper, or anything the parser cannot read, does not pass silently: it is recorded as a parse error, and blocked if you choose parse_error: block.
About 950 chained NOTs, roughly 4 KB of SQL, overflow a recursive parser's stack and kill the process running it. Vericto measures the text's nesting before parsing it and refuses anything past 200 levels: the proxy stays up and the statement is recorded as too complex (blocked under parse_error: block).
In 6 public incidents we documented, the destructive SQL (the published statement, or the one the mechanism implies) is BLOCKED by these rules when the connection goes through Vericto: a DELETE FROM on every production table, DROP TABLE requested from text-to-SQL frameworks (two CVEs), a schema push that dropped tables, COPY … TO PROGRAM on a "read-only" MCP server and a COMMIT; DROP SCHEMA that escaped a read-only transaction. The cases, with their sources.
Start wherever there's least friction: TCP proxy, Runtime API, CLI, Validation API or MCP. All five call the same deterministic AST engine, so the verdict is the same through any of them.
DELETE has no WHERE. English narration, with English and Spanish captions.Five modes over the same engine. Two act at runtime and block inline; three act before execution, in your pipeline or in the agent's editor. How to choose.
Proxy TCPjust change the connection string host; blocks inlineRuntime APIyour application asks before running; also Oracle, SQL Server, Snowflake and SQLiteCLIvalidates in pre-commit and CI, with an exit code by verdictValidation APIbatches of SQL over HTTPS, nothing to installMCPthe agent validates the SQL while it writes itEach query is parsed into its syntax tree: with pg_query (the Postgres parser) for Postgres and with sqlparser-rs for MySQL, Oracle, SQL Server, Snowflake and SQLite. The full tree, not just the first token or text patterns. The same engine in all five modes, so the verdict does not depend on where the statement came in.
Queries that violate the ruleset are blocked with the offending AST node, the triggered rule and the suggested safe version. At runtime the statement never reaches the database; before execution, the verdict comes back as an exit code or as the agent's response. Clean ones pass untouched.
DELETE FROM users
SELECT * FROM users WHERE id = $1
Two ways in. On PostgreSQL and MySQL, the TCP proxy needs no code changes. On all six databases, the SDKs, the Runtime API, the CLI and MCP check SQL before it runs.
Point your connection string at the proxy. It works with any driver or ORM and blocks destructive queries inline, before they reach the database.
Set up the proxy →The Python and Node SDKs and the Runtime API check each query before your code runs it. The CLI and MCP check SQL before it ships.
vericto-dbt check reviews compiled models in CIcheck_sql for Claude Code, Kiro and morevericto/check-sql action annotates findings on the PRvericto init with --target gitlabNot on the list? Any PostgreSQL or MySQL driver works through the proxy, and the Runtime API works from any language. See all integrations →
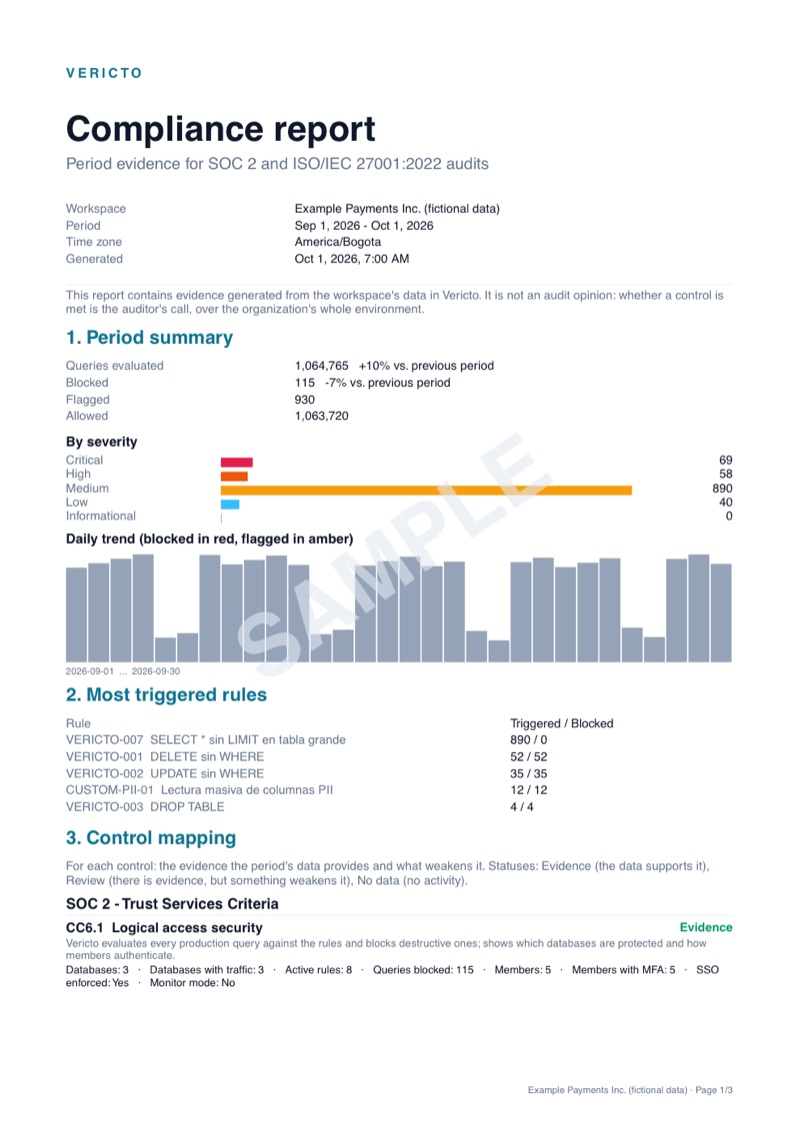
What Vericto blocks and records in production is already the evidence a SOC 2 or ISO 27001 auditor asks for. Vericto delivers it ready to read, and signed:
Prices exclude tax. Any VAT, GST or sales tax due in your country is added at checkout.
Billed annually, Builder is $63/month and Team $199/month.
Connect your first database in less than 5 minutes.




Deterministic and verifiable. We don't ask for blind trust.
Vericto does not use AI to decide what to block. The engine, the proxy and the CLI are public source, and every claim on this page can be checked.
Public source
The AST engine, the TCP proxy and the CLI, on GitHub, source-available under the Functional Source License (FSL-1.1-ALv2), which becomes Apache-2.0 two years after each version: vericto-engine, vericto-proxy, vericto-cli.
CLI on npm
Install it and check your migrations against your rules:
@vericto/vericto-cliEvidence you can verify offline
Compliance reports are signed with Ed25519 and your auditor checks the signature with the public key, with no account and no network. How to verify them.
Public changelog and status
Every release, with what changed and why, in the changelog. Service availability on the status page.
+0.42 ms
What the proxy added at p50 on PostgreSQL with 1 connection, measured on staging on October 16, 2026 (vericto-proxy 4.12.0, 0.25 vCPU ARM64 task, Aurora Serverless v2 at 10 ACU, TLS, enforce mode). A measurement, not a guarantee: conditions and method.
Deterministic
The same query with the same rules always gets the same verdict. Before you enforce a rule, the simulator shows which legitimate flows it would block.