What your auditor gets
Six pieces of evidence that build themselves while Vericto protects your databases.
Immutable audit trail
Every query evaluated, with the decision, rule, severity and AST node. No one can edit or delete it by hand.
Signed PDF report
Next to every CSV or JSON export: period summary, most triggered rules, controls and configuration, signed with Ed25519.
Control mapping
The period's activity related to 6 SOC 2 criteria and 6 ISO 27001 controls, with what weakens them.
Daily configuration snapshot
Which rules, policies, members and API keys were in force each day, and what changed between snapshots.
Automatic monthly report
On Enterprise, the signed report for the previous month arrives on the 1st of each month, kept 13 months or what your contract sets.
Verifiable offline
Your auditor checks the signature with Vericto's public key, with no account or network: any change to the file invalidates it.
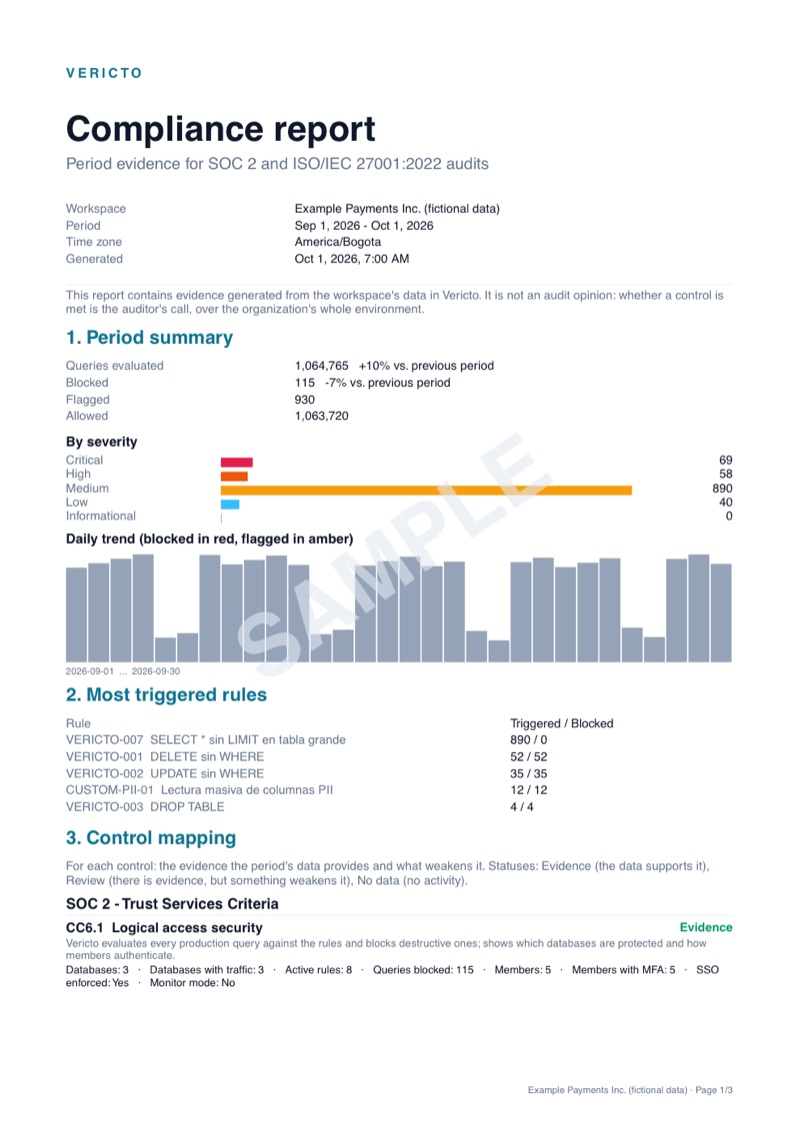
This is what the report looks like
The sample is generated by the same code as real reports, over a fictional workspace during September 2026. It has three pages:
- Period summary: queries evaluated, blocked and flagged, by severity, with their daily trend and the comparison with the previous period.
- Control mapping: each criterion with its evidence and status, including what the auditor should review.
- Configuration: what was in force at the start and end of the month, and every change in between.
Fictional data, marked SAMPLE and unsigned. Real reports come with their .sig file.
Controls it provides evidence for
The dashboard's Controls tab and section 3 of the report relate each period's activity to these controls.
| SOC 2 | Evidence Vericto provides |
|---|---|
CC6.1 Logical access security | Every production query evaluated against the rules; which databases are protected and how members authenticate (MFA, SSO) |
CC6.2 User registration and authorization | Who joined the workspace, and with which role, during the period |
CC6.3 Access modification and removal | Members removed, API keys revoked and active keys without an expiry date |
CC7.2 Monitoring for anomalies | Every blocked or flagged query, and failed logins |
CC7.3 Evaluation of security events | Blocked queries are contained, with the AST node and severity; alerts notify the team |
CC8.1 Change management | Configuration changes detected, and migrations validated in CI before reaching production |
| ISO/IEC 27001:2022 | Annex A control |
|---|---|
A.5.18 | Access rights |
A.8.2 | Privileged access rights |
A.8.3 | Information access restriction |
A.8.15 | Logging |
A.8.16 | Monitoring activities |
A.8.32 | Change management |
What each plan includes
| Builder | Team | Enterprise | |
|---|---|---|---|
| Audit trail and Controls tab | |||
| Query history | 30 days | 90 days | Unlimited or per contract |
| CSV/JSON export signed with Ed25519 | — | ||
| PDF report with every export | — | ||
| Automatic monthly report | — | — | 13 months or per contract |
| Enforced SSO (OIDC) | — | — | |
| Support during the audit | — | — |
About scope: Vericto produces evidence for the listed controls; it is not an audit opinion. Whether a control is met is your auditor's call, over your organization's whole environment. Vericto, as a company, is in the process of SOC 2 certification and does not have its own report yet. If your vendor review needs it, write to enterprise@vericto.com.
More detail in Audit trail, Verify reports and How to use the audit trail in a SOC 2 audit.